HIPAA News

Your #1 source for info about HIPAA, HIPAA compliance, HIPAA privacy and the latest HIPAA lawsuits

  • Home
  • Archives
  • Links
  • RSS Feed
  • Follow @hipaanews on Twitter
  • Follow HIPAA News on LinkedIn
  • Like HIPAA News on Facebook

New York-Presbyterian Accidentally Posts HIPAA Protected Patient Data Online

September 28, 2010 by melanierivera

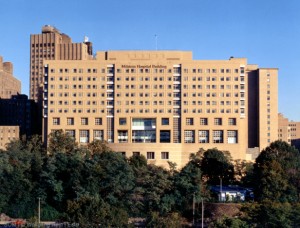
In “another day, another privacy breach” news it was revealed this week that the venerable New York-Presbyterian Hospital and Columbia University Medical Center “inadvertently” posted the personal medical data of thousands of its patients online  in July of this year.

Information about around 6,800 patients was posted and much of it included names, addresses, clinical data and in ten cases social security numbers.

When the breach occurred it was caught by the eagle eye of patient’s relative who came across the data online, meaning it was picked up by search engines. No announcement about the error was made at the time the institution says because an internal investigation was being conducted.

Although a great deal of information was revealed, including patient temperatures, a spokeswoman for the hospital Myrna Manners told The Times that no diagnosis information of any kind had been disclosed (that’s OK Mrs Jones, they have your name address and phone number but no one knows you had a hip replacement)

According to Manners the data was accidentally placed on a server and has since been removed.

“We deeply regret that this has occurred and we understand the concern that patients and their families may feel upon learning that their information may have been exposed,” the hospital said. “We are in the process of informing all affected patients and have set up a hot line for patients to call if they have questions.”

Apparently no one knows exactly how the sensitive data ended up on the server. The hospital says there’s absolutely no evidence the information has been “improperly used,” but it has not disclosed whether it knows how many people might have seen the information.

Share this:

  • Tweet

Related

Posted in: HIPAA News, HIPAA Regulations Tagged: HIPAA privacy breach, New York-Presbyterian HIPPA breech, Patient data exposed, privacy breech

Subscribe to new HIPAANews.net posts via Email:

Enter your email address:

Delivered by FeedBurner

RSS feed: Latest HIPAA News from Around the Web Latest HIPAA News from Around the Web

  • HHS Secures Six-Figure HIPAA Settlements With Employer-Sponsored Group Health Plans – Davis Wright Tremaine October 29, 2026
  • Brandy Mabra on using AI safely without risking HIPAA – Rolling Out October 29, 2026
  • GoodRx & Criteo Revised $32 Million Data Privacy Settlement Gets First Approval October 29, 2026
  • Hospital Ransomware Attacker Receives 70 Month Jail Term – The HIPAA Journal October 29, 2026
  • Hospital Ransomware Attacker Receives 70 Month Jail Term October 29, 2026
  • Writing Privacy Rules Patients Can Trust – Wilson Sonsini October 29, 2026
  • AdvaMed Data Access: 4 Rules Medtech Must Follow [2026] – shattered.io October 29, 2026
  • A HIPAA Security Risk Assessment Checklist Small Practices Actually Use (2026) – BBN Times October 28, 2026
  • Score HIPAA Cloud Backup Services: 13 Steps, 30 Days [2026] – tech-insider.org October 28, 2026
  • Is It a HIPAA Violation to Enter Patient Information Into ChatGPT? – Attack of the Fanboy October 28, 2026

Recent Posts

  • General Data Protection Regulation (GDPR) Compliance
  • Doc Vader on ER Misuse
  • HIPAA Privacy Complaints
  • 2017 is Raising the Bar for Annual HIPAA Breaches
  • Ensuring Availability of HIPAA During Natural Disasters

RSS feed: HIPAA Book Reviews HIPAA Book Reviews

  • HIPAA video
  • 11 Years of HIPAA and it’s still not easy for consumers
  • HIPAA Checklists
  • Five Essential HIPAA Books for Beginners
  • Top 10 highest-rated HIPAA books for IT Managers

Copyright © 2026 HIPAA News.

Lifestyle WordPress Theme by themehit.com